Security
How your patients' data is protected
The patient information you keep in Klinikbook is yours. This page explains in plain words where it is kept, who can see it and how it is protected. The legal details are in the security overview and the data processing agreement.
At a glance
Servers in Germany
All data is kept on Contabo servers. The databases and files run on private networks the internet cannot reach.
Each workspace kept apart
In the application and by row-level security in the database itself.
Private files
Documents and photos open only through links that expire within minutes.
Two-step sign-in
With an authenticator app; your workspace can require it of everyone.
Support only with your permission
Our staff never open your patient records, and look inside only when you grant access.
Daily backups
The databases are backed up every day and the backups are kept for 14 days.
Where the data lives
Every Klinikbook server runs at Contabo, in Germany.
- The databases, queues, caches and files run on the servers' private networks and cannot be reached from the internet.
- Every connection from the internet passes through Cloudflare's protected network and is encrypted (TLS); browsers are told to use encrypted connections only (HSTS).
- For customers in Türkiye, servers abroad mean a transfer under article 9 of the KVKK; the Türkiye pack of the compliance center states it in your privacy notice.
- The providers that run parts of the service - hosting, network protection and e-mail delivery - are named on the sub-processor list.
Each workspace kept apart
One clinic can never reach another clinic's records.
- Records are separated twice: in the application, and by row-level security in the database itself. Even if the application made a mistake, a request for one workspace could not read another's records.
- Trying the address of a workspace you are not a member of gets the same answer as an address that does not exist, so not even its existence is revealed.
- Patients reach only their own records through the portal, and your partners' guests see only the trips you share with them.
Documents and photos
Patient photos and documents are the most sensitive things a clinic stores, and they are handled that way.
- Photos and documents are kept in private storage and have no public address.
- A file opens only through a link that expires within minutes.
- Every uploaded file is checked to be the format it claims to be, and documents are scanned for malware before they are stored.
Sign-in and sessions
A stolen password alone should not open your workspace.
- Passwords are stored only as salted hashes (PBKDF2), and repeated wrong attempts lock the account for a while.
- Two-step sign-in with an authenticator app, with one-time recovery codes. It is recommended to everyone, and a workspace can require it of every member.
- Klinikbook's own staff always sign in with a second factor.
- Sessions end after a period without activity, and everyone signs in again at least every two weeks. You can end your sessions from your account.
- The account's owner is told by e-mail whenever two-step sign-in is turned on or off, or the recovery codes are renewed.
Roles and permissions
Each person sees what their work needs.
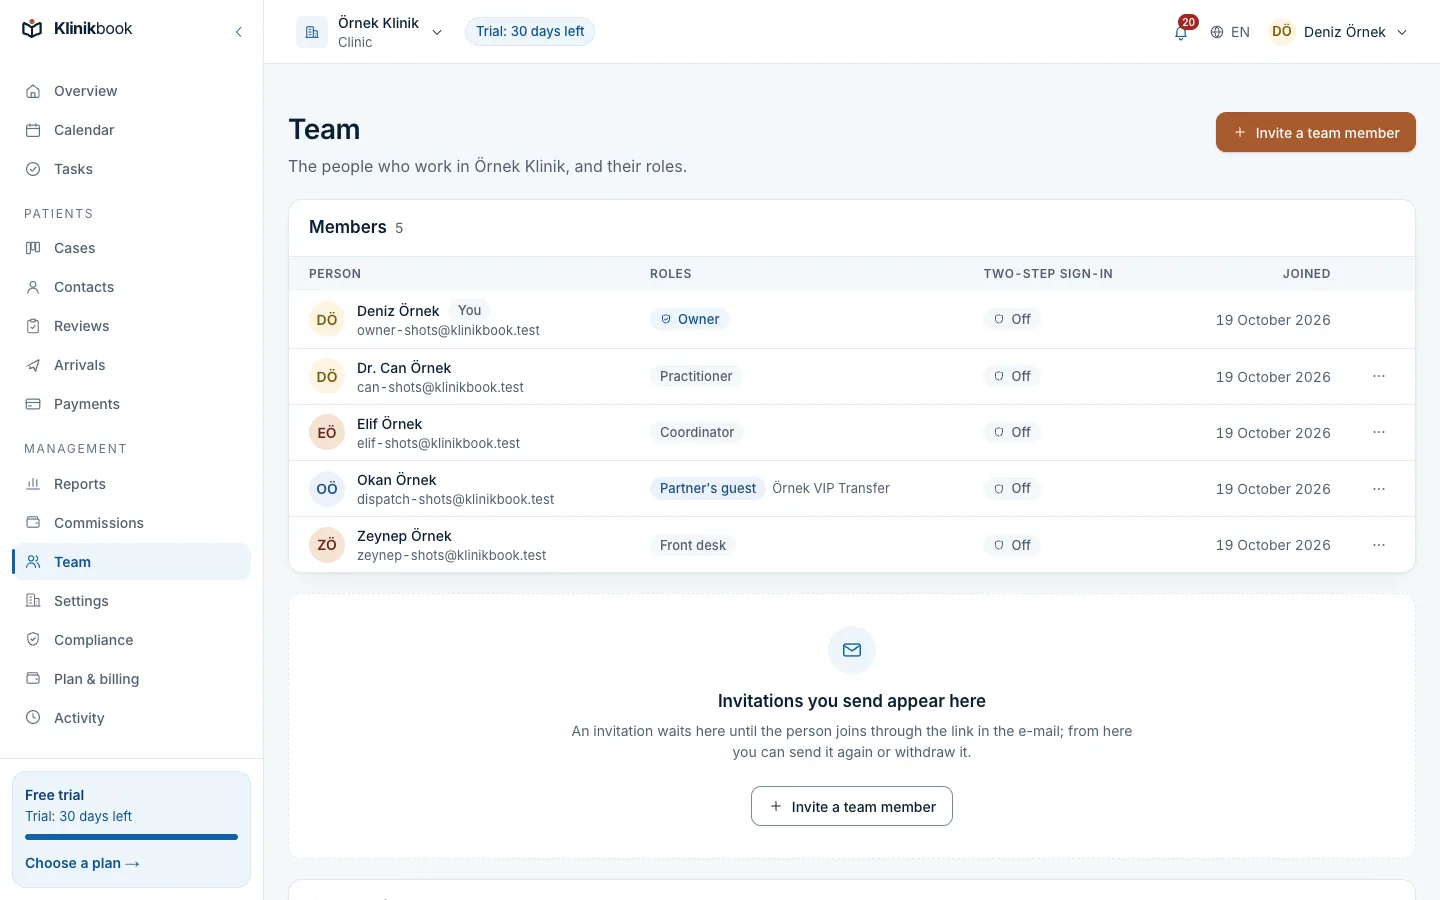
- Roles decide who sees and does what: owner, administrator, coordinator, practitioner, front desk, finance, marketing, read-only and partner guest.
- A practitioner sees their own cases and the reviews sent to them; finance sees the payments ledger without reading the cases.
- A quote's internal costs are shown only to people with that permission.
- A workspace has one owner, and ownership changes only by a transfer the new owner accepts.
Activity log and support access
You can see what happens in your workspace, including anything our staff do.
- Significant actions in a workspace are written to its activity log, which you can export as CSV.
- Klinikbook staff do not open your workspace's patient records.
- When you need support, the owner or an administrator grants access with a purpose and a duration of 1 to 72 hours. The grant is visible in the workspace and can be ended at any time.
- During it our staff read only the activity log - never a patient record - and every look is written both to the platform's audit trail and to your own log.
- Access to the servers is limited to authorised staff, uses personal keys and is recorded.
Tools for KVKK and GDPR
For your patients' data you are the controller and Klinikbook is your processor. The compliance center gives you the tools to meet your duties.
- Country packs for Türkiye and the EU/UK: privacy notice and explicit consent templates filled in with your details, published in versions on your patient portal.
- Photo and video use and marketing consent templates, with every consent decision recorded.
- Data subject requests: a copy of the person's data as a zip file, correction, erasure, restriction of processing and objection, with a notice to the person.
- A retention policy that erases, once the period you set has passed, people who never became patients and whose cases were all closed as lost.
- The data processing agreement, accepted by the workspace owner, and the published sub-processor list.
- Klinikbook gives no legal advice: have the texts checked by a lawyer against your own situation.
Backups, and when you leave
Your data stays yours, also on the way out.
- The databases are backed up every day, and the backups are kept for 14 days.
- The owner can download, at any time, one zip file with every record and file of the workspace; the file is kept for 7 days.
- The owner can close the workspace. A workspace that ends without a plan has its data deleted from every part of Klinikbook after 90 days, and the backups expire 14 days later. Klinikbook's own invoices are kept for the period the law requires.
What Klinikbook never does
Some lines are part of how Klinikbook is built, not settings.
- It does not sell your data, use it for advertising or process it for its own purposes.
- It does not contact your patients on its own account.
- It does not touch patients' money: payments go straight from the patient to you.
- It does not look inside your workspace without your grant, and does not open patient records even with one.
- It is not a marketplace: it does not list you to patients, send you patients or take a commission.
- It does not claim a security certification it does not hold.
The documents
This page is a plain summary. The binding texts are these documents.
- Security overviewThe measures in place, as a legal text.
- Data Processing AgreementHow Klinikbook processes data on your behalf (KVKK article 12, GDPR article 28).
- Sub-processor listThe providers that run parts of the service, and where.
- Privacy policyHow Klinikbook handles the data of its own customers and visitors.
Incidents and reports
If a security incident affects personal data in a workspace, we tell its owner without undue delay, where possible within 48 hours, as the data processing agreement describes.
If you find a security weakness, please write to [email protected] with “Security” in the subject before disclosing it. We answer and keep you informed while we fix it.
Try Klinikbook with your own team
Every feature is open for 30 days, and no card is needed to start.